Be Ready Before a Cyber Incident Happens: Strengthening Cyber Resilience with Blackpanda IR-1
Cyber incidents rarely happen at a convenient time.
A ransomware attack, compromised endpoint or suspicious network activity can quickly disrupt operations and put sensitive information at risk. When an incident happens, the first few hours are critical. Organisations need to know who to contact, what actions to take and how quickly specialist support can begin.
That is why cyber resilience is not only about preventing attacks. It is also about being prepared to respond and recover when an incident occurs.
ATech, together with Blackpanda, helps organisations strengthen this readiness with Blackpanda IR-1, an incident response retainer designed to provide rapid access to cybersecurity incident response and digital forensics expertise.
Why Incident Response Readiness Matters
Many organisations already invest in firewalls, endpoint protection, monitoring and other cybersecurity technologies. However, technology alone cannot eliminate every cyber risk.
When an incident occurs, teams can suddenly face difficult questions:
- What has been compromised?
- How far has the attack spread?
- Should affected systems be isolated immediately?
- How can evidence be preserved for investigation?
- How can operations be restored safely?
- Who should coordinate the incident response?
Trying to answer these questions for the first time during an active cyber incident can slow down containment and recovery.
A prepared incident response plan gives organisations a clearer path forward.
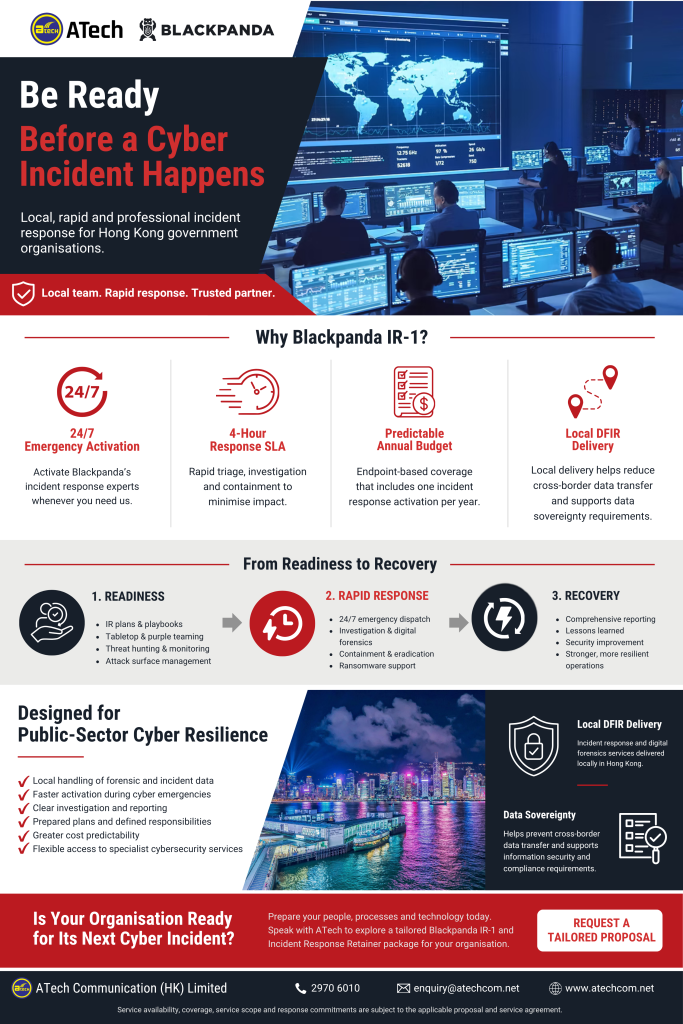
Blackpanda IR-1: From Readiness to Recovery
Blackpanda IR-1 supports organisations across three important stages of cyber incident management.
1. Readiness
Preparation starts before an incident happens.
Blackpanda can support organisations with incident response plans and playbooks, tabletop and purple-team exercises, threat hunting and monitoring, and attack surface management.
These activities help teams understand responsibilities, identify potential weaknesses and establish procedures before they are needed in a real emergency.
2. Rapid Response
When an incident occurs, speed matters.
Blackpanda IR-1 provides 24/7 emergency activation with a 4-hour response SLA, helping organisations quickly access incident response expertise for triage, investigation and containment.
Response capabilities highlighted in the service include:
- 24/7 emergency dispatch
- Incident investigation and digital forensics
- Containment and eradication
- Ransomware support
Instead of searching for specialist assistance after an attack has already begun, organisations have a predefined response arrangement ready to activate.
3. Recovery
Incident response does not finish when the immediate threat has been contained.
Blackpanda also supports post-incident recovery through comprehensive reporting, lessons learned and security improvement recommendations. This helps organisations understand what happened and use those findings to strengthen future cyber resilience.
Local Response for Hong Kong Organisations
For Hong Kong organisations, particularly government and public-sector environments, how incident and forensic data is handled can be just as important as response speed.
Blackpanda IR-1 offers local digital forensics and incident response delivery in Hong Kong, helping reduce unnecessary cross-border transfer of incident data and supporting data sovereignty and organisational compliance requirements.
A local response model can also provide:
✓ Faster activation during cyber emergencies
✓ Local handling of forensic and incident data
✓ Clearer investigation and reporting
✓ Prepared responsibilities and response procedures
✓ Greater cost predictability
✓ Access to specialist cybersecurity expertise when required
More Predictable Incident Response Planning
Cyber incidents are unpredictable. Cybersecurity budgeting should not have to be.
Blackpanda IR-1 provides endpoint-based coverage that includes one incident response activation per year, allowing organisations to incorporate incident response capabilities into their cybersecurity planning with greater budget predictability.
Combined with 24/7 activation and a 4-hour response SLA, organisations can establish an incident response capability before an emergency occurs, rather than negotiating support while systems may already be under attack.
References and Further Reading:
Read More about January 2026 Newsletter: https://www.atechcom.net/blog/atech-newsletter-jan26/
Read More about February 2026 Newsletter: https://www.atechcom.net/blog/atech-newsletter-feb26/
About ATech Communication (HK) Limited
ATech Communication (HK) Ltd is one of the leading IT equipment & service provides for HKSAR Government Departments and Bureaux. We provide the best value and the best IT solution to our customers. Please visit our Cases page to learn more about our successful works. For more information on ATech, please contact us at enquiry@atechcom.net.
ATech Communication (HK) Limited
Providing a Complete Suite of IT Solutions
- (852) 2970 6010 / 3756 0078
- enquiry@atechcom.net